A01
Rooted Android with MagiskValidated
A Magisk-rooted phone reports compromised with four signals: bootloader_unlocked and three root signals.
How to read this page
A scenario is one test case: prepare the environment, run the steps, then compare the expected result (written before the run) with the observed result (copied from the run, with screenshots).
- A01 · A
- Run on a real phone that's been attacked or modified — rooted, jailbroken, hooked or hidden.
- Validated
- Run, and the result matched what was expected.
Why it matters
Proves detection, not just the absence of false positives.
Environment
- App
- Example app, library 0.3.0
- Device
- OnePlus Nord 3 (CPH2493), Android 15 (CPH2493_15.0.0.1601, patch 2026-01-01)
- Root
- Magisk 31.0, bootloader unlocked (verified boot: orange)
Setup
Prepare the environment.Then run the steps.
- 01Root the device with Magisk (see the Android testing guide).
- 02Install the example app.
- 03Leave the app out of the DenyList (no hiding).
Steps
What to run.What to read.
- 01Open the app.
- 02Read the status badge and the signal list.
Expected result · written before the run
Status: compromised4 signals.
root_magisk_files fires through the app's own mount table (Magisk's magisk tmpfs mounts). bootloader_unlocked fires with the default bootloaderUnlocked setting.
Observed result · copied from the run
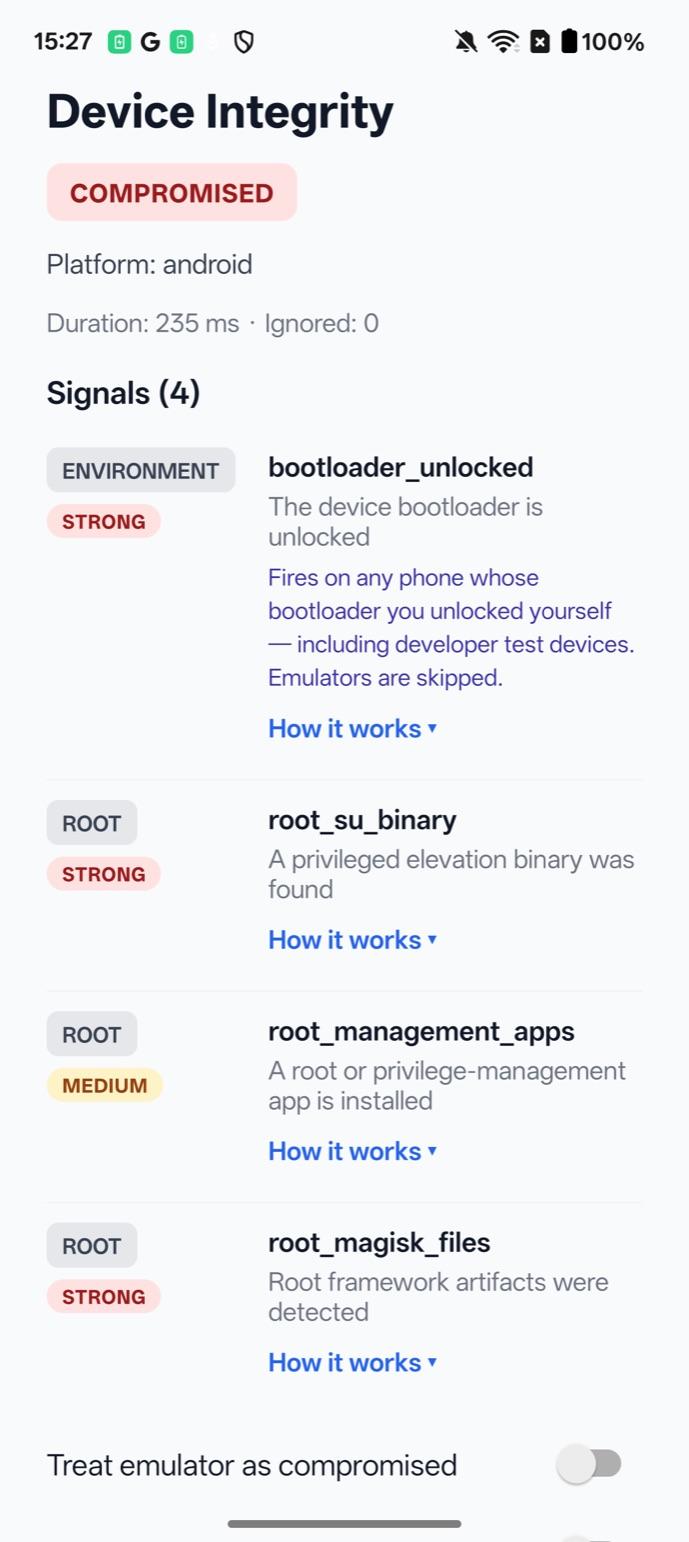
Status: compromisedObserved 2026-10-06.
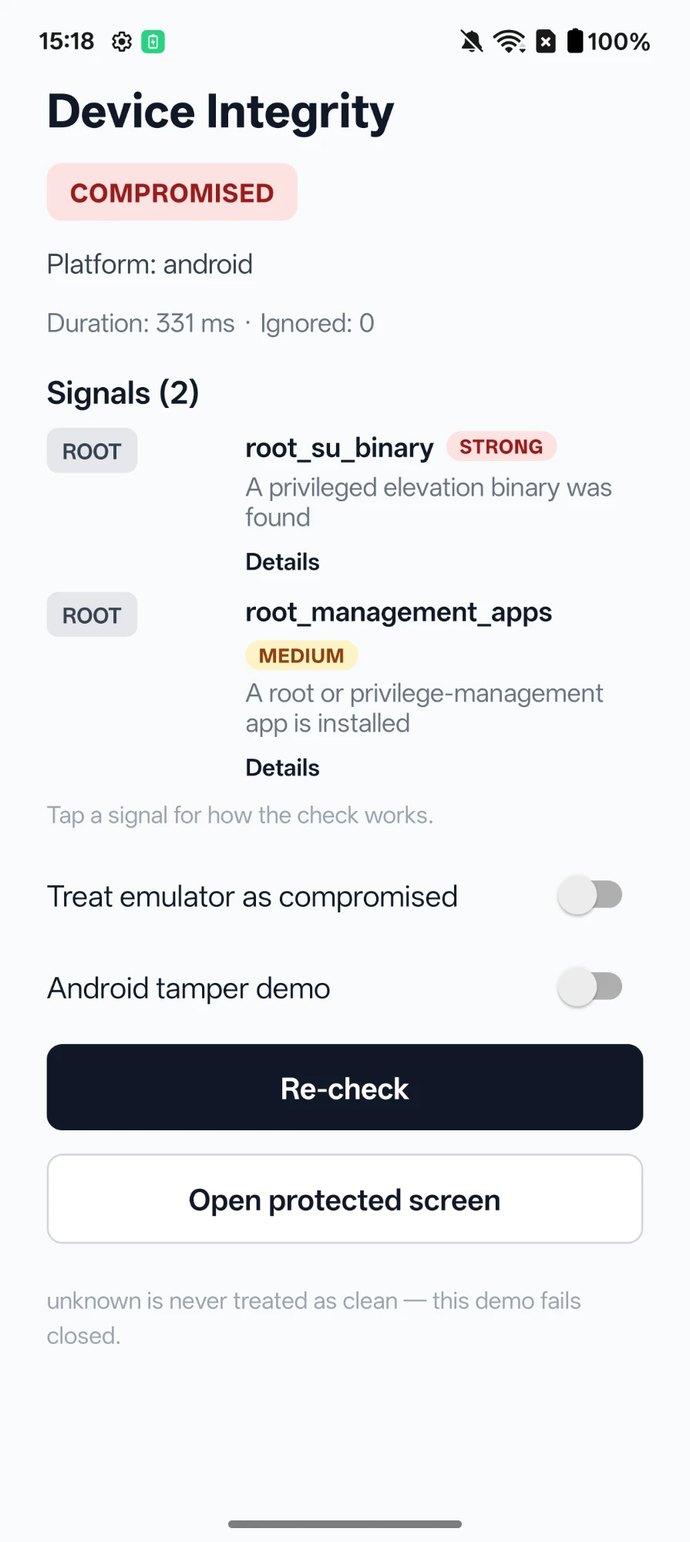
su was found at /product/bin/su (Magisk's mount), com.topjohnwu.magisk is installed, /proc/self/mountinfo lists Magisk's tmpfs mounts, and ro.boot.verifiedbootstate is orange. On library 0.2.1 (2026-10-02, second screenshot) the same phone reported only root_su_binary and root_management_apps: root_magisk_files checked fixed paths only, and /data/adb/magisk is unreadable to an app — the gap 0.3.0 fixed. Re-run on 2026-10-06 after the Android speed-up (library 0.3.2: system properties read in-process instead of spawning getprop, one /proc/self/maps read, no per-line regex on /proc/mounts), A/B on the same phone, release build, three cold starts each: 0.3.0 took 124–140 ms, 0.3.2 36–46 ms, with the same four signals every time (first screenshot). The 235 ms above is a debug build.
Status: COMPROMISED · Duration: 235 ms · Ignored: 0 · Signals (4) · [environment] bootloader_unlocked: The device bootloader is unlocked · [root] root_su_binary: A privileged elevation binary was found · [root] root_management_apps: A root or privilege-management app is installed · [root] root_magisk_files: Root framework artifacts were detected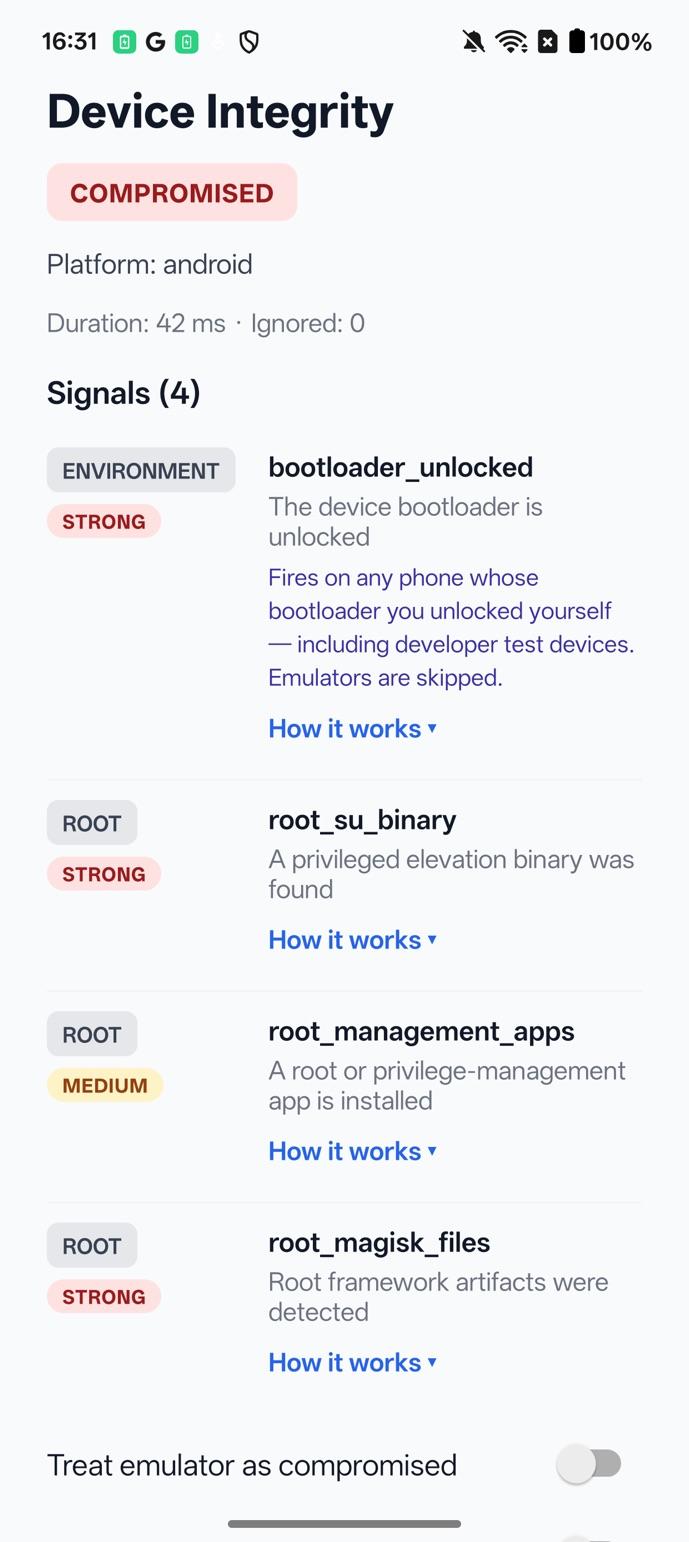
Checks this scenario covers
Every check this test case touches — including ones that aren't expected to fire here. The expected and observed results above say which ones should and did. Each links to how the check works.